
29 April 2026
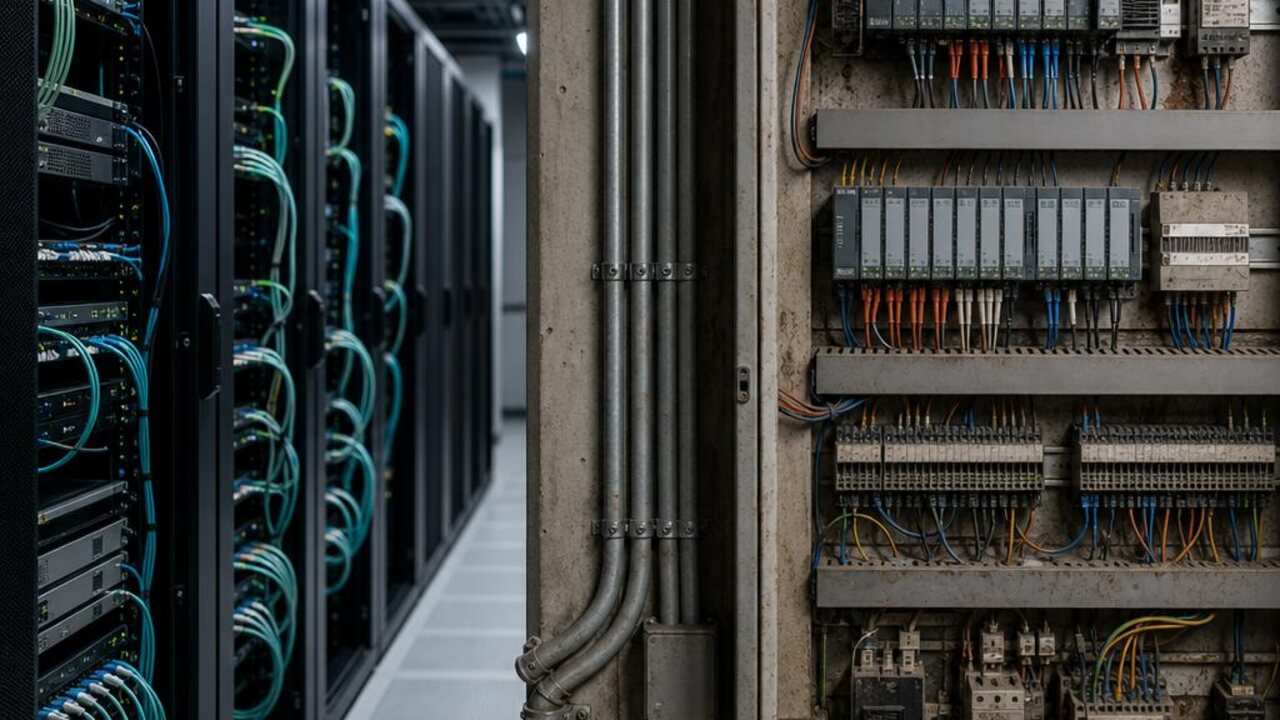
Different worlds, same words
IT security protects information: confidentiality first, on hardware refreshed every few years, patched monthly and rebooted at will. OT security protects physical processes: safety and availability first, on control systems that run for twenty or thirty years, often cannot be patched without a plant shutdown, and must never be destabilised by the security tooling itself.
Where IT assumptions break
Standard IT practices can be actively dangerous in OT. Aggressive network scanning has crashed controllers built long before such traffic existed. Agent software cannot be installed on proprietary control hardware. Forced patching windows collide with continuous processes that cost enormously to stop. Even encryption can conflict with the deterministic timing industrial protocols expect.
What OT security uses instead
The OT toolbox is architectural: zone-and-conduit segmentation that contains an intrusion, unidirectional gateways where data must flow out but never in, passive monitoring that learns normal process behaviour and flags deviation, compensating controls around unpatchable systems, and rigorous control of the remote-access paths through which most real incidents arrive.
One organisation, two disciplines
The practical failure mode is organisational: IT teams applying IT reflexes to plants they do not operate, and engineers treating security as an outside imposition. Operators that succeed create a joint capability (engineering knowledge of the process, security knowledge of the adversary) and buy tooling built for OT rather than adapted to it.
The bottom line for programme owners
For defence and critical-infrastructure buyers, the decisive move is to stop procuring OT security as an extension of the IT catalogue. Tools that assume frequent patching, agent installation and aggressive scanning can actively endanger the process they are meant to protect, and buying them wastes budget on an approach that industrial environments reject. The advantage lies with programmes that pair process engineers and security specialists under one accountable owner, then select tooling purpose-built for OT (passive monitoring, zone-and-conduit segmentation, controlled remote access) rather than IT products relabelled for the plant floor. Vetting the supplier of that tooling matters as much as its features, since it will live inside long-lived control systems. Owners who get this right protect availability and safety without importing IT's fragility into the physical world.
